intake.
Tell us who you are, what to test, and what already keeps you up at night. Domain, a founder LinkedIn, and one app URL are enough to start.
openhat security.
we're a modern offensive security company, powered by ai to combat an ai-scale attack surface.
let us penetration test your systems for a $1,000 flat fee upfront, if we don't find anything critical, you get your money back. Our turnaround is 24-72 hours. If we do find a critical vulnerability, we provide a step-by-step remediation guide.
root@your-company-server:~# ohqs engage --authorized
how an engagement goes.
Short path from intake to findings. Not a consulting menu. We don't sell snake oil.
Tell us who you are, what to test, and what already keeps you up at night. Domain, a founder LinkedIn, and one app URL are enough to start.
You pay the package fee and sign off so we can touch your systems. No permission, no work.
Our side: recon and OSINT, ai playbooks and smoke tests, then sensitive actions by hand. Full logs of everything we touched.
If we land a Critical, you get a step-by-step remediation guide plus a clear report. If we don't, the engagement is free — and you still get a report of what we probed.
our method.
We start with what you give us — not a cheat sheet. ai finds and curates; humans take the sensitive shots.
We start with your domain, company name, and the basics you share. Creative OSINT — no cheating with private docs you did not hand over.
Automated ai playbook generation plus smoke testing. A detailed guide of what to do and where to look before anything sensitive runs.
Sensitive actions happen with care, by hand, after ai finds and curates them. Full logs of everything we touched.
free arsenal.
a majority of our offensive security tools are open source and available to the public free of charge. ru a nerd? get started now.
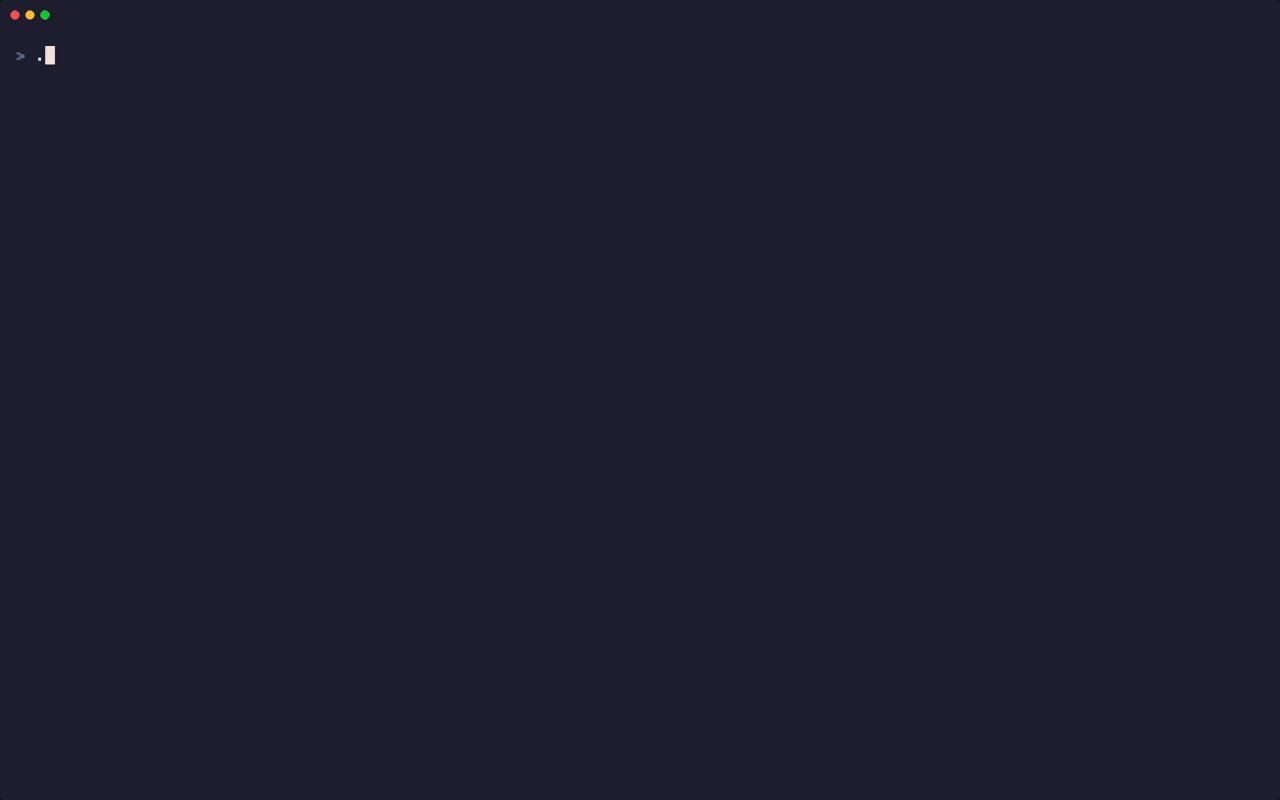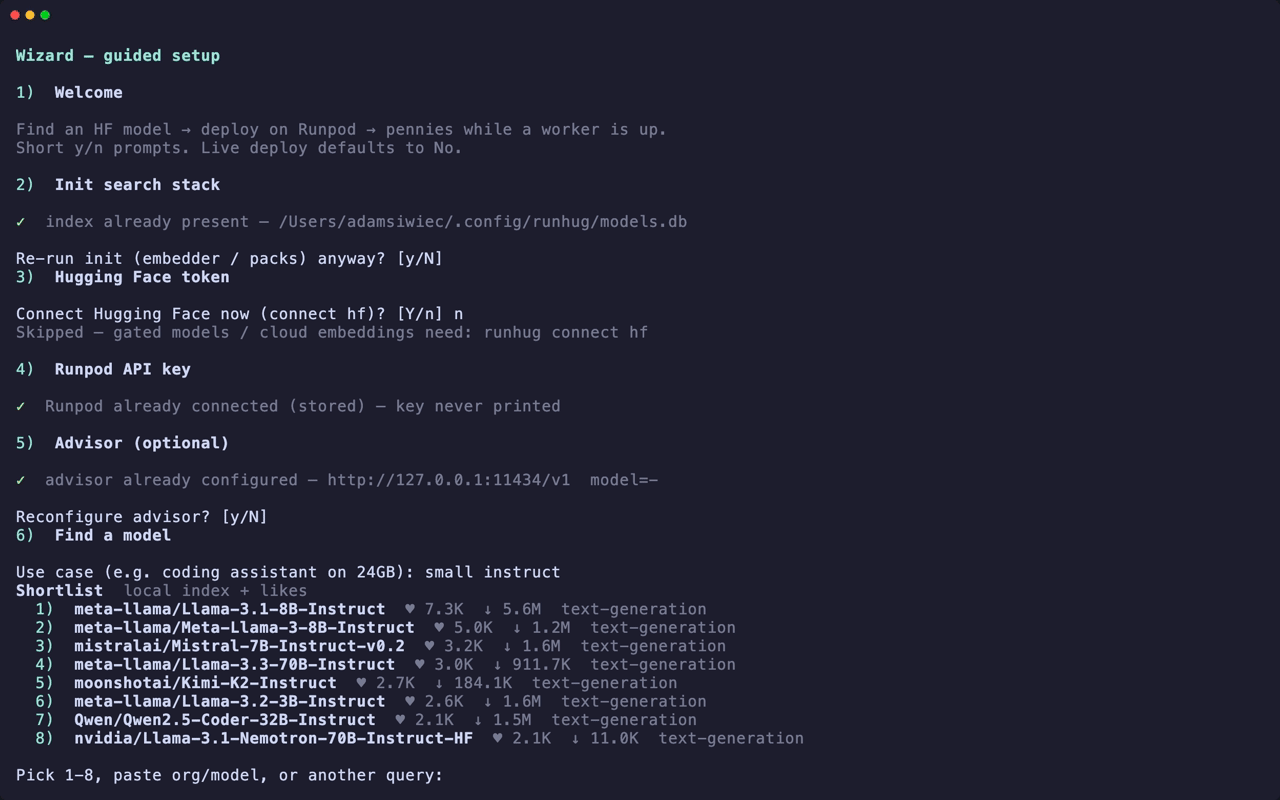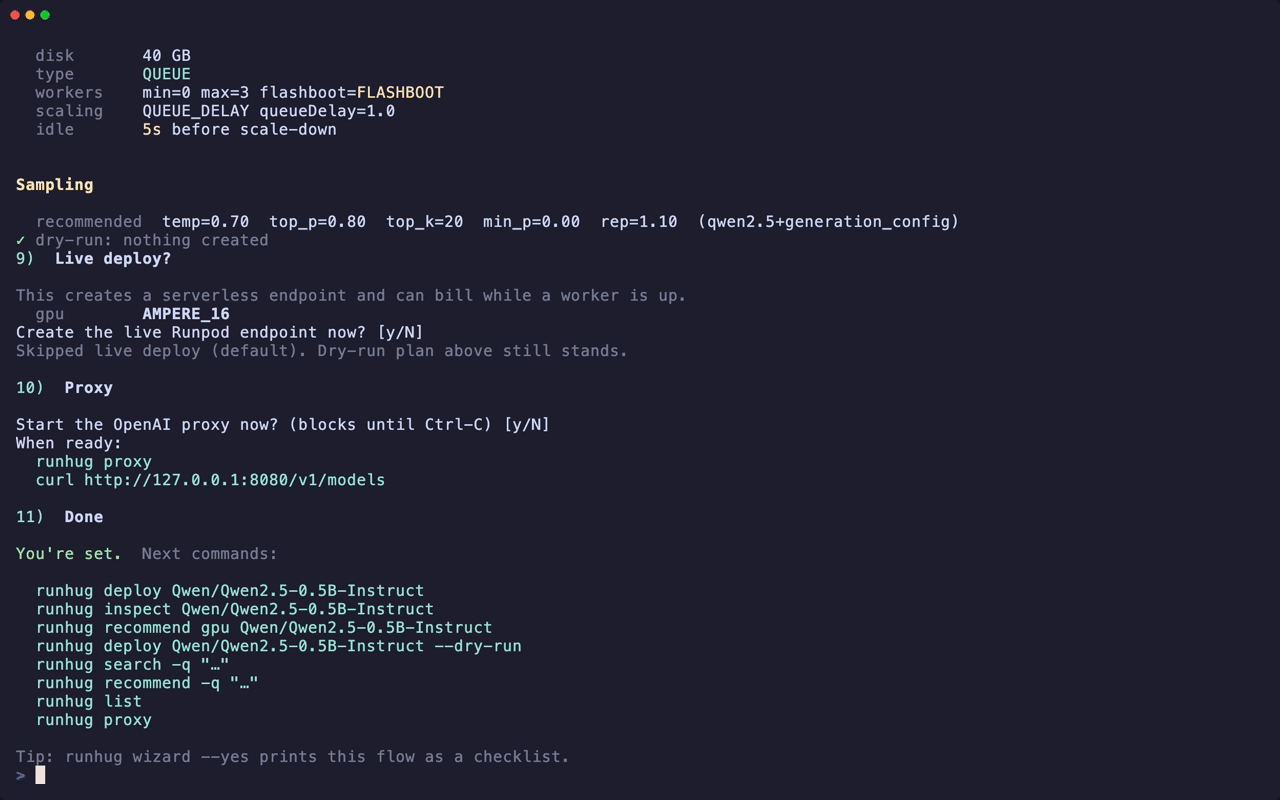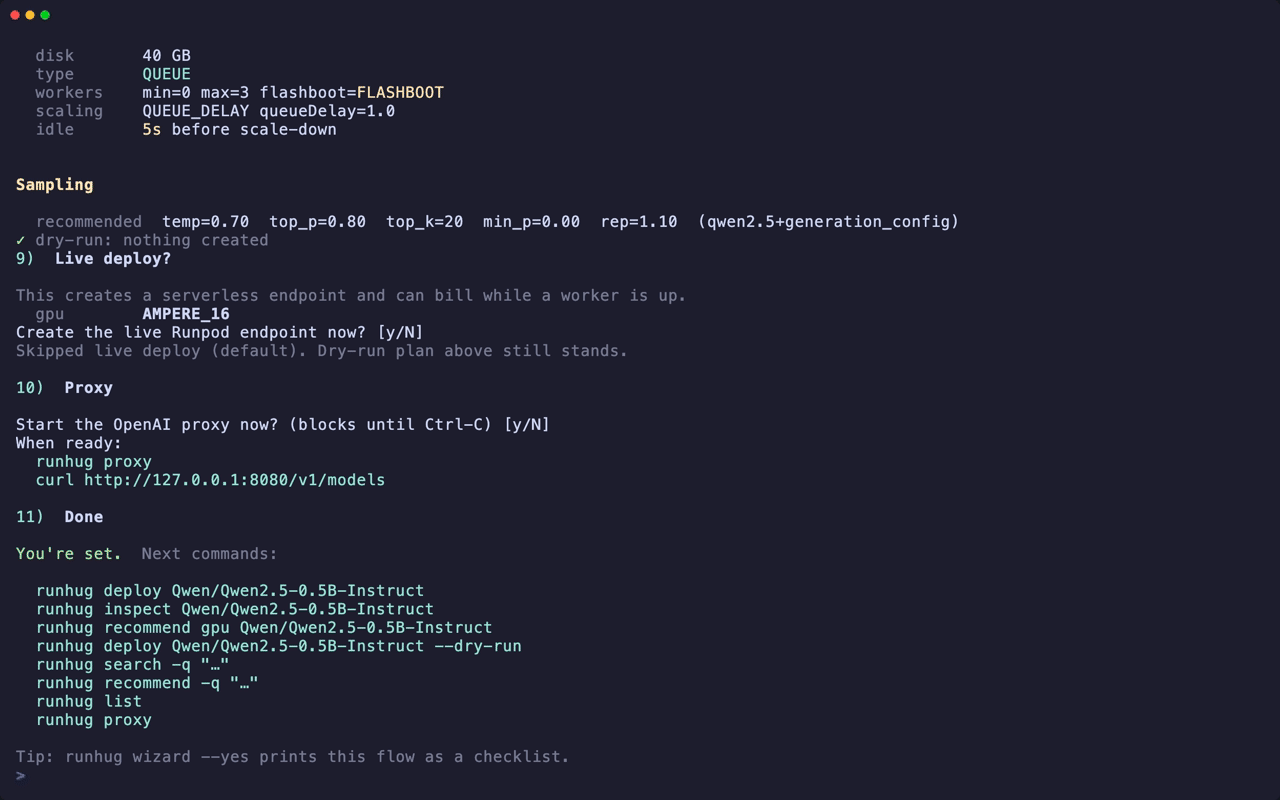
openhat-security/runhug
Find the best Hugging Face model. Deploy on RunPod or GCP in minutes. Run it for pennies. https://runhug.devrecated.com https://www.youtube.com/watch?v=WEnywc8ZJl8
openhat-security/ohqs
ohqs
live preview →
openhat-security/ohqs
OpenHat quickstart - use AI to quickstart your penetration test or ethical hacking exploit. Core tool utilized within our proprietary product, provided to the community as FOSS.
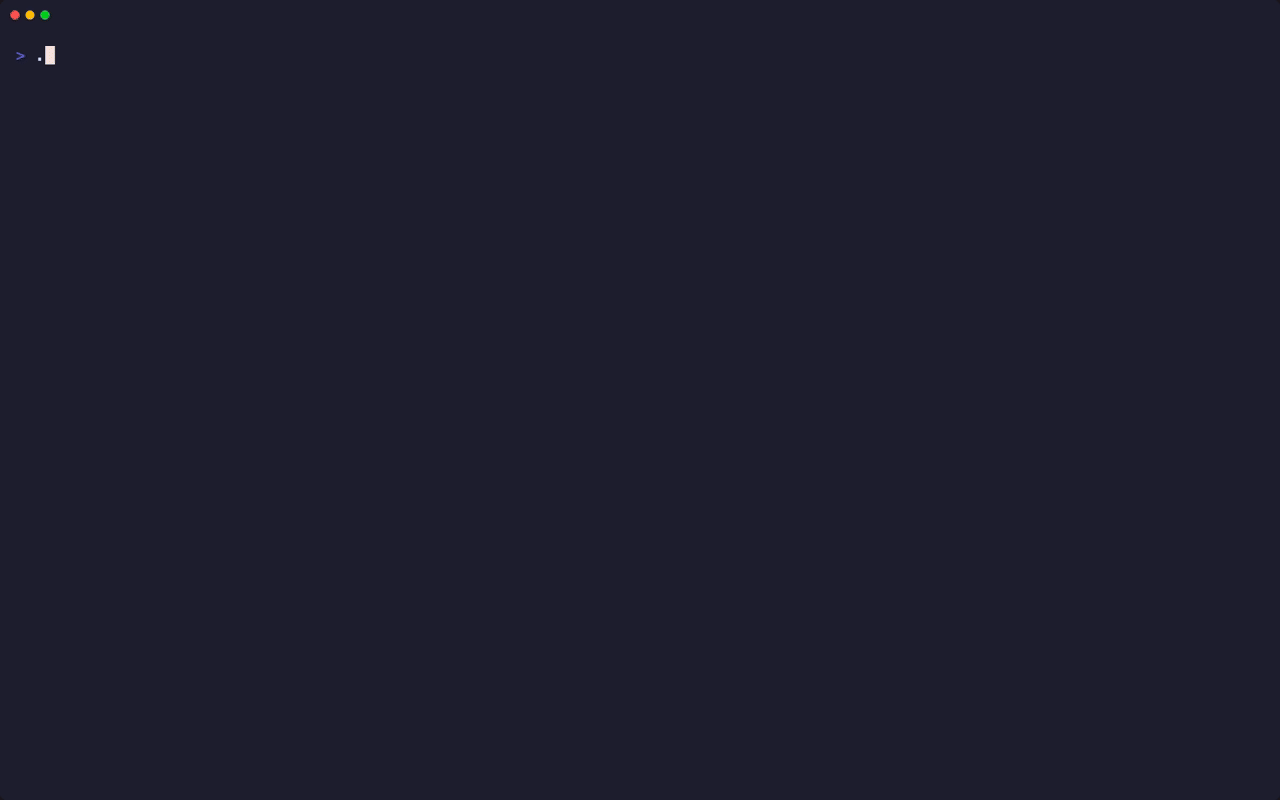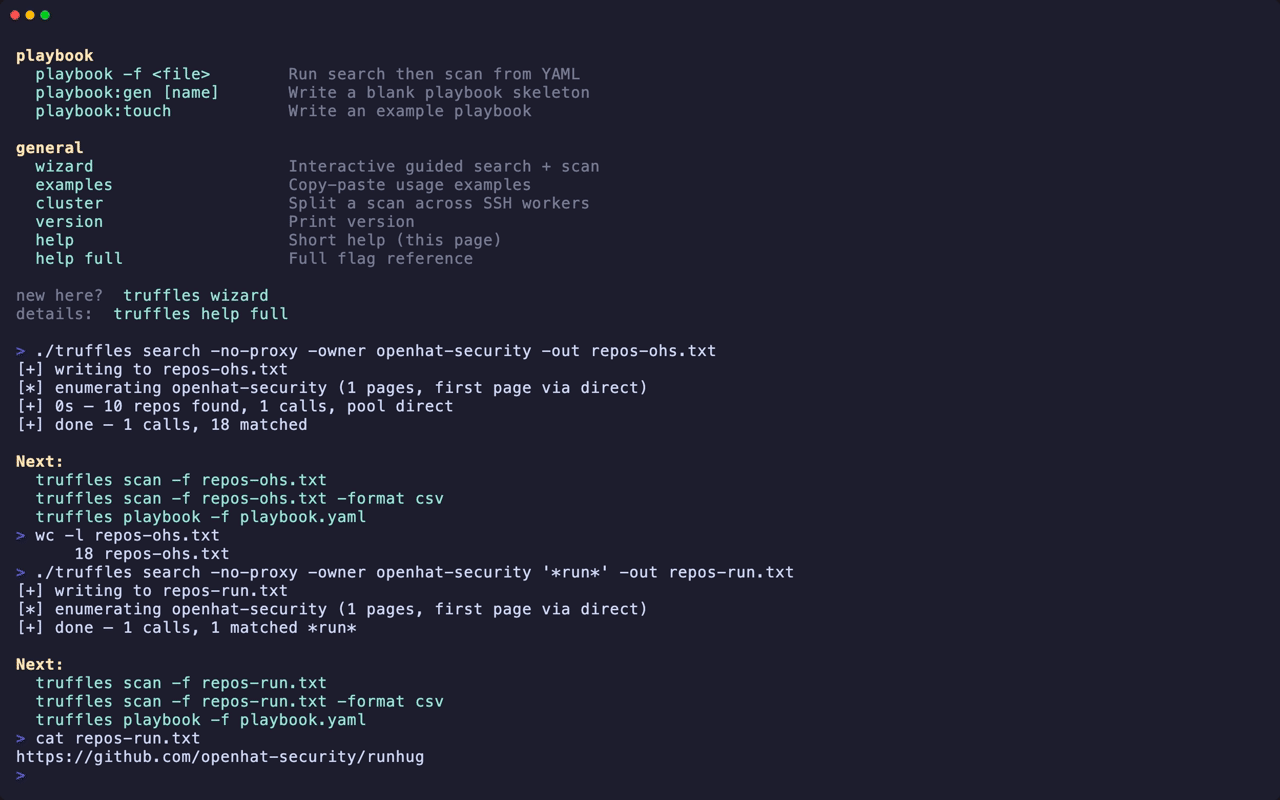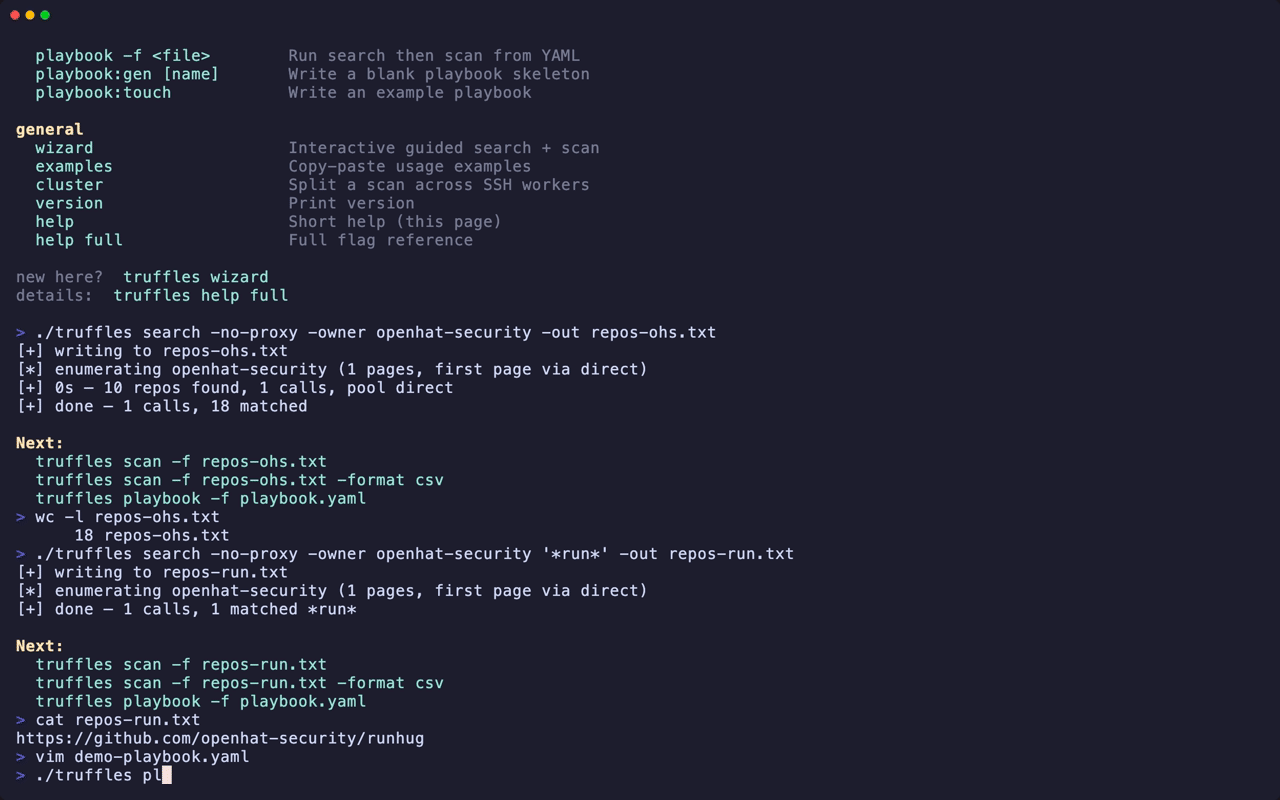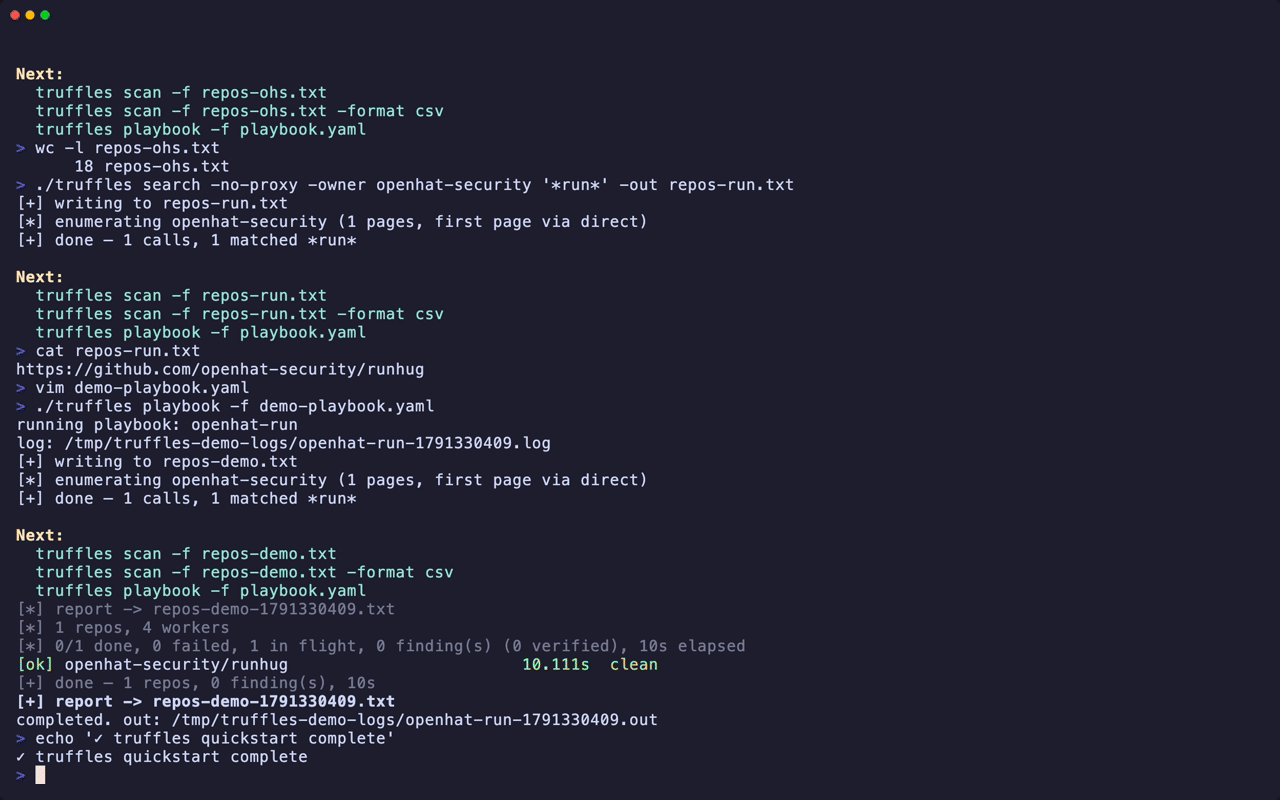
openhat-security/truffles
Find GitHub repos at scale. Scan every commit. Catch leaked secrets. https://truffles.devrecated.com
operator note.
“everyday more ai slop makes it into the code me and you use day to day. yeah.. software might be cheaper to build. as we know...there's always a catch or hidden cost. we combat this by using AI to combat AI-scale attack surfaces. no...your in-house engineer can't do this. not for a reasonable cost at least. i spent way too much time figuring out how to make this work. let us help you.”
next step.
Domain, company, one app URL, and written permission. Flat fee, 24–72 hour turnaround, remediation guide if we land a Critical — fee back if we don't.